
MASTR research
BlockLayerPod and BeaconLayerPod: the interview invitation
MASTR's archived research follows the social-engineering stage before a wallet loss.
Research articles and reference entries are published in English. Navigation is available in seven languages.
In this article
The approach
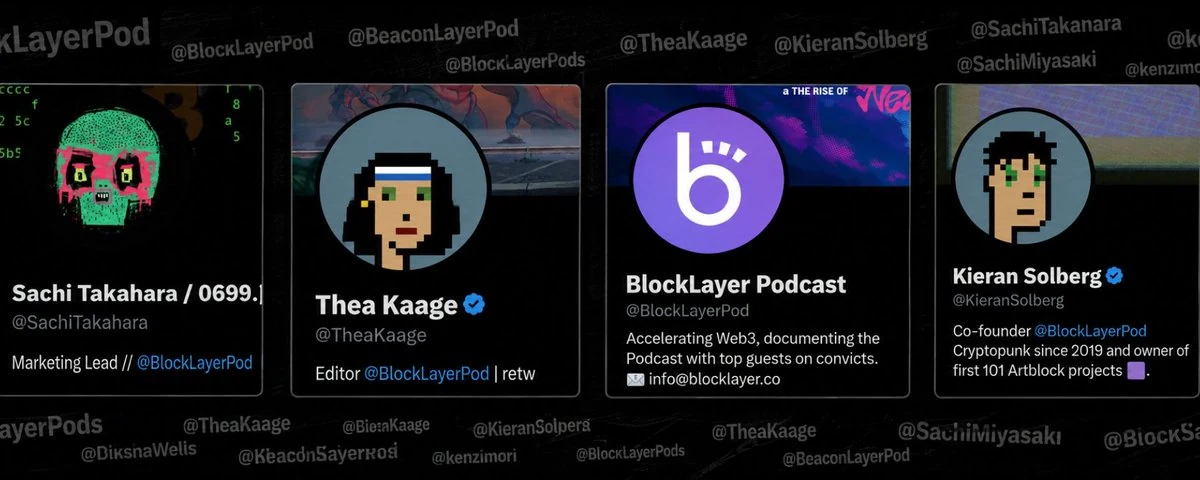
MASTR's attention-capture essay describes a phishing model using BlockLayerPod and BeaconLayerPod identities. Creators, developers and other visible Web3 participants received personalised podcast or interview invitations. Professional profiles, scheduling links and preparation instructions made the contact resemble an ordinary work opportunity.
- 01 · InvitationA plausible professional contact
A profile and a proposed interview establish a reason to keep talking.
- 02 · PreparationAn unexpected technical requirement
The contact asks for unfamiliar software or an unexplained command.
- 03 · DecisionVerify the action independently
A convincing identity does not make a device-access request safe.
- 04 · If software ranUse a clean device for account access
Preserve the invitation and installation details for incident review.
Pattern described in MASTR’s archived research. This is a social-engineering sequence, not attribution to an identified operator.
The decisive change came when preparation required an unexpected installation, terminal action or unfamiliar meeting tool. The apparent business relationship was being used to obtain access to a device, credentials or wallet environment. A final blockchain transfer would show only the last part of that process.
Why the preparation stage matters
A victim may already have checked a profile and agreed to an interview before the suspicious request arrives. Cancelling then feels costly: time has been reserved, the invitation sounds flattering and the other party may claim the meeting is about to begin. That context can make an unreasonable technical request feel like a small administrative step.
Keep the contact's identity and the requested computer action as separate questions. A legitimate interview does not require importing a recovery phrase or running unexplained commands. Confirm an invitation through an independently established channel and use familiar meeting software obtained from its official source.
The archive's limits
MASTR's historical case summary records the approach, rather than a complete list of associated accounts. Names and infrastructure can be replaced, and copied identities do not identify the people operating them. The recurring pattern is the escalation from professional trust to device access.
If suspicious software has already run, stop using that device for wallet or account access and consult the incident-response guide.
Preserve the invitation before the account disappears
Save the original message, profile URL, timestamps, scheduling page and the exact request that changed the nature of the meeting. A screenshot helps preserve appearance, but a copied URL and the original message retain details that may not be visible in the image. Record whether the request was to visit a page, install software, grant a permission or run a command. These actions create different exposure and should not be collapsed into a single claim that a wallet was hacked.
If no installation or wallet action occurred, record that too. An attempted approach is still worth documenting, but it is not evidence of a completed compromise. The archived MASTR case concerns how the invitation created trust; a report on a later incident would need its own device and transaction evidence.
Assess the requested action separately from the caller
A useful verification question is whether the meeting can proceed through a familiar service without the requested installation. Contact the claimed organisation through a channel established independently of the invitation. Do not use a second account suggested by the same caller as independent verification. A profile’s history may be informative, but copied branding and a professional-looking calendar do not explain why access to a device is necessary.
Keep any evidence collection proportionate to the situation. The objective is to preserve what happened and establish exposure, not to interact further with a suspected operator or test their software on a computer holding valuable accounts. The original source below supports the historical description; these paragraphs explain how to document a similar approach.
Sources
Research checked 5 September 2026. Historical cases retain the date and legal status of the cited record.